
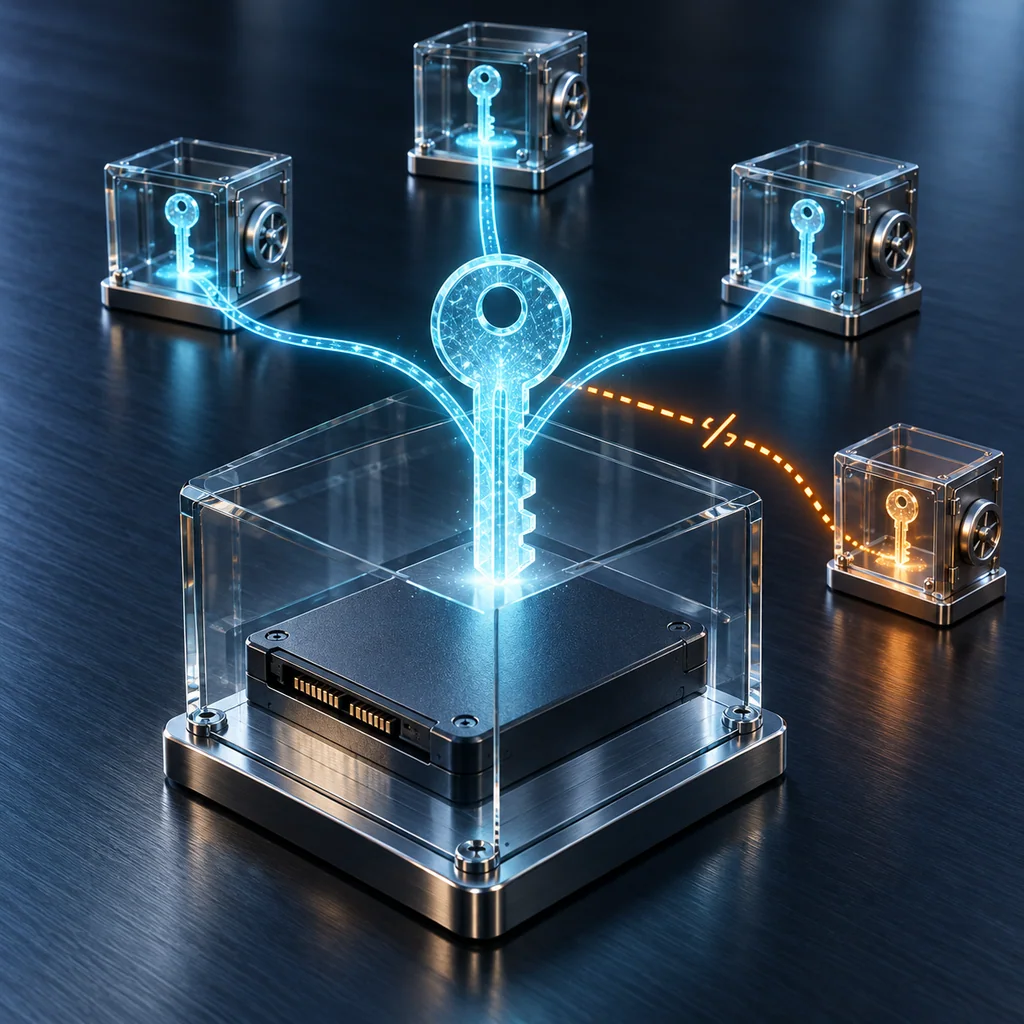
Cryptographic Erase: Key Copies and Recovery Paths
Short answer
Cryptographic erase is credible only when the target data was appropriately encrypted and every relevant route to its decryption has been addressed. Deleting a password, disabling an account or removing one key record does not establish that condition. Follow the data-encryption key, the keys that protect it, and any copies that can restore either.
Start with a scope question: are you sanitizing one device, one encrypted volume, or all copies of a dataset? A successful device-level operation does not delete an independently decryptable backup elsewhere.
Who this is for
Storage engineers, security reviewers and ITAD teams evaluating cryptographic erase as part of an authorized sanitization process. The concrete software example concerns conventional software-encrypted LUKS containers using cryptsetup 2.8.1 documentation. OPAL-backed LUKS and device-internal self-encrypting-drive operations have different behavior and must be assessed separately.
When to use this
Use it when considering crypto erase for a retiring device, writing acceptance requirements for a key-management service, or reviewing a job that reports key deletion but has incomplete backup history.
When not to use this
Do not rely on this method alone if sensitive plaintext may predate encryption, the relevant key history is unknown, an implementation cannot establish what keys it removes, or policy rejects the residual ciphertext risk. Route those conditions to a suitable alternative or additional method; do not conceal them under a large key-size claim.
This guide is not an instruction to destroy operational keys. Authorization, retention obligations and recovery approval precede any irreversible action.
Workflow
1. Define the ciphertext and its history
List the storage objects in scope and the intervals during which they held sensitive information. Record when encryption began and whether an earlier appropriate sanitization established a clean starting point. A volume encrypted today may still have a history that requires a different treatment.
Separate encrypted data from plaintext exports, application caches and other storage outside the encrypted boundary. Their deletion needs its own disposition. The purpose is a bounded claim: identify what a particular crypto-erase action can affect, rather than declaring an entire organization's information deleted.
NIST SP 800-88 Rev. 2, published September 2025 and superseding Rev. 1, is the guidance baseline here. It treats cryptographic implementation, key sanitization and traceability as necessary parts of evaluating this method. Its publication status was checked for this guide; it is not a product certification.
2. Identify the level at which deletion occurs
The data-encryption key protects data. A key-encryption or wrapping key protects another key. A passphrase can authorize recovery of key material without being the data key itself. Document those roles instead of using “the password” for all three.
Deleting a wrapping key may close a recovery route only under the actual implementation's assumptions. Ask whether another wrapper, an unwrapped copy or a retained lower-level key remains. A diagram with one key icon is insufficient evidence for a system with several recovery paths.
A proposed evidence worksheet can use the following fields:
Data object and encryption epoch
Key role and non-secret identifier
Wrapper or derivation dependency
Known copies and recovery mechanisms
Responsible custodian
Planned sanitization evidence
Unresolved exceptions and disposition
This is an author-designed review aid, not a cryptographic proof or a standard-mandated schema. Do not put key values or recovery secrets in it.
3. Follow a concrete LUKS backup counterexample
In cryptsetup 2.8.1, the documented erase action removes active LUKS keyslots rather than overwriting the encrypted data area. For conventional software LUKS, retaining an earlier header-and-keyslot backup can defeat the conclusion that erasing the current header alone made the data unrecoverable.
The backup plus a passphrase valid when that backup was taken can still enable decryption, even after that passphrase was changed or removed on the live volume. A password-change ticket therefore cannot, by itself, close the historical-backup question.
This is not the same as saying the backup contains plaintext data. It preserves a recovery mechanism for ciphertext that is still available. Nor should this software example be generalized to OPAL-backed encryption: the documented hardware-key removal path has different recovery semantics.
No destructive command is supplied here. Before using a real tool, match its version and encryption backend to the approved procedure and complete the backup review.
4. Assign evidence to every recovery custodian
Ask the device operator about local recovery material, the backup owner about retained header copies, and the key-management owner about external key recovery. Keep responses tied to non-secret key identifiers, storage objects and dates.
For a hypothetical volume with a current header, an old header backup and an external recovery copy, a receipt covering only the current header leaves two unresolved questions. Do not convert those unknowns into a percentage of completion: the remaining path may be sufficient for recovery.
The reviewer should distinguish “copy not found in the searched location,” “retention expiry scheduled,” and “sanitization completed with evidence.” They represent different claims. A queued deletion is not a completed operation.
Where multiple assets share key dependencies, check the impact before eliminating anything. Resolving one retirement request must not make unrelated retained data unavailable. The approved scope and service-owner decision control the action.
5. Address copies already in use
A key removed from persistent storage may previously have been unwrapped into active cryptographic machinery. Define how the implementation stops further use and handles that live material. Use its documented mechanism rather than inventing a universal waiting period or power-off guarantee.
Similarly, revoking a user's login can restrict access without sanitizing the underlying key. That may be a useful security action, but record it accurately. Re-enabling an account or restoring a service backup must not silently restore the recovery path that the erase decision assumed was gone.
6. Execute only after the evidence boundary is clear
The authorized operator should run the qualified method and retain its completion/error evidence. If one custodian cannot establish the disposition of a relevant copy, keep the exception explicit. Options include a suitable additional media treatment, a narrower claim with an approved retention boundary, or holding the asset for review.
Do not describe a key deletion as permanent merely because a current decrypt attempt fails. The failure could reflect missing credentials, a disconnected service or the wrong metadata, rather than successful key sanitization.
Verification checklist
- Data scope, encryption history and plaintext exceptions are defined.
- The implementation and backend match the proposed operation.
- Key roles, dependencies and relevant copies are accounted for.
- External custodians provide evidence rather than deletion promises.
- Live-use and restoration paths have explicit dispositions.
- Errors and unknowns remain visible in the acceptance decision.
Verification should establish that the intended operation ran and expose its limits. Validation asks whether the accumulated evidence is adequate for the intended release. Neither is replaced by an algorithm name or elapsed time.
Resale and evidence checklist
Retain a restricted record linking asset identity, encryption implementation, key-sanitization action, external-copy scope, exceptions and approval. If backups are intentionally retained, state whether they fall outside this device's sanitization claim and how their continuing confidentiality is governed.
A certificate should not say “all data copies destroyed” when it documents only the retirement of a single encrypted drive.
What not to publish
Never include raw keys, passphrases, header backups, tokens, recovery packages or customer-identifying key labels in a public report. Use a redacted process example; keep the actual evidence in the authorized restricted system.
Common mistakes
Equating password rotation with key destruction; forgetting an old header backup; treating scheduled expiry as completed deletion; assuming every encrypted byte has always been encrypted; and using brute-force arithmetic to dismiss an available recovery key all skip implementation evidence.
CliDeck workflow fit
A reviewed runbook can assign the key-copy questions to named custodians and preserve approval checkpoints alongside the asset record. No support, certification or capability of forthcoming wiping software is implied by this process guide.
FAQ
Does crypto erase overwrite the ciphertext?
Not necessarily. The objective is to make decryption infeasible through key sanitization. The actual operation and its prerequisites depend on the implementation.
Is an encrypted backup automatically covered by deleting the drive's key?
No. Determine its encryption and recovery dependencies. A separately decryptable backup needs a separately scoped decision.
Can a failed decrypt attempt prove all keys are gone?
No. It tests a particular attempted recovery path under its current conditions. It does not enumerate every possible retained copy or restoration route.
Related guides
Verification note: review criteria, not a claimed erase trial
The scenarios and worksheet are illustrative. No keys, headers, volumes or drives were erased or tested for this article. The checklist defines evidence to obtain in an authorized workflow; no customer logs or measured recovery outcomes are claimed.